A data breach at Trezor’s shipping partner, ShipMonk, has exposed the personal information of approximately 13,700 customers, prompting a re-examination of the security considerations surrounding hardware cryptocurrency wallets. The incident underscores risks associated with the physical logistics and third-party vendor involvement in hardware wallet distribution, extending security concerns beyond the management of private keys.
Breach Details and Exposed Information
The breach, disclosed by Trezor on August 13, involved unauthorized access to ShipMonk systems that held customer order data. The exposed information includes names, phone numbers, and home addresses of recent Trezor customers. ShipMonk first notified Trezor about the unauthorized access on Monday, August 10. Importantly, Trezor has stated that its devices themselves were not compromised in this incident.
Re-evaluating Hardware Wallet Risks
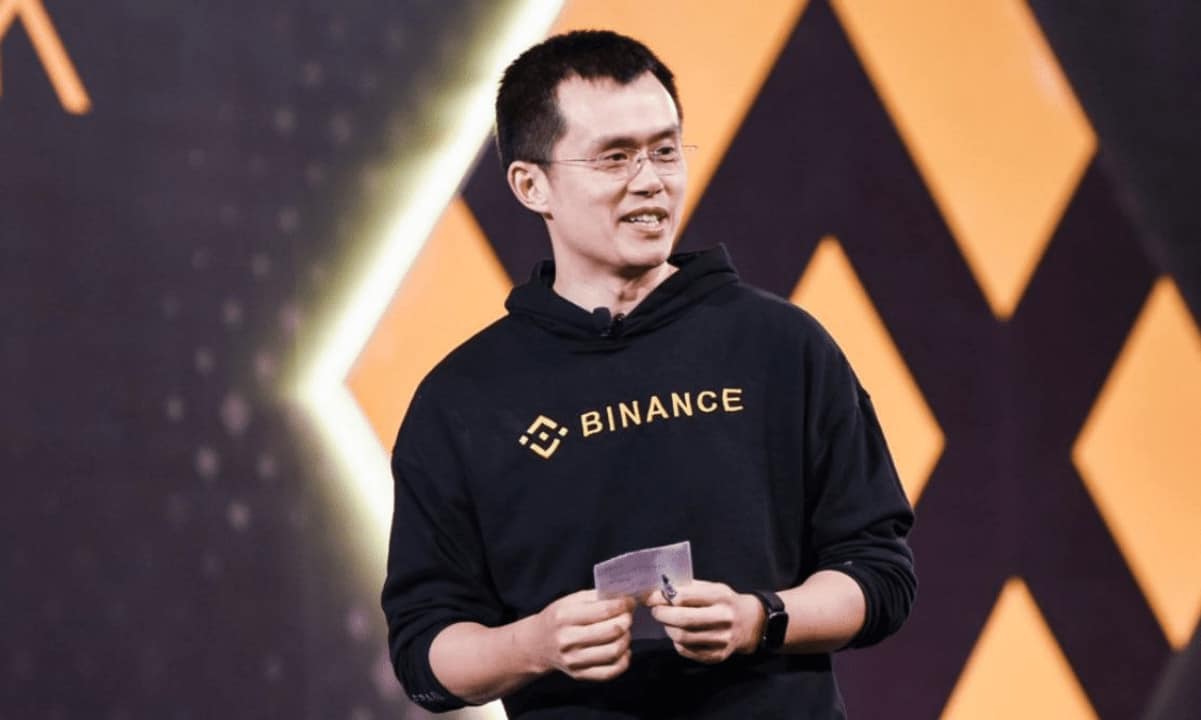
In the wake of the breach, Binance founder Changpeng Zhao (CZ) highlighted what he described as a “real advantage” of software self-custody wallets. CZ argued that software wallets avoid the risks tied to shipping physical devices that link a user’s identity and address to their cryptocurrency holdings. He noted that while hardware wallets have specific advantages, this incident underscores a different risk profile compared to software alternatives like the Binance Web3 Wallet or Trust Wallet, which do not involve shipping physical products.
Broader Security Landscape and Expert Warnings
Security experts have warned that the exposed data could be used for sophisticated phishing attacks, social engineering, or even physical threats. Nick Neuman cautioned that the data could lead to targeted social engineering and potentially wrench attacks, while NaoX Protocol stated that exposed addresses could identify crypto holders for direct targeting. Trezor has advised its customers to be vigilant against potential phishing attempts via email, phone calls, or letters, and stressed the importance of never entering wallet backups online or sharing them.
This incident is not the first time Trezor has faced security concerns related to third-party vendors. In January 2024, a separate breach involving a Trezor third-party support vendor exposed contact details for around 66,000 users. Furthermore, the broader hardware wallet ecosystem has seen recent scrutiny. In mid-July, pseudonymous crypto investigator ZachXBT criticized hardware wallets as “complete garbage” for serious use, suggesting that a spare phone used solely for signing transactions might be a more secure alternative. Additionally, Galaxy Research has linked over $100 million in stolen Bitcoin to a firmware issue in older Coldcard devices.
Implications for Users
The ShipMonk breach underscores that the security of hardware wallets extends to the supply chain and data handling practices of their partners. The incident prompts a re-evaluation of the overall security model for self-custody, considering risks beyond the digital realm. Users are reminded to remain cautious and follow best practices for securing their cryptocurrency assets, regardless of the wallet type they choose.
Broader Context
Source materials place the factual news in this context: The incident involves a data breach at Trezor’s shipping partner, ShipMonk.
Leave a Reply